How Scammers Clone Shopify Stores (and How to Catch Them in the First Week)
Copies of an online store look improvised. They are not. The same sequence appears often enough to write down, and each step has a reason that follows from the economics.
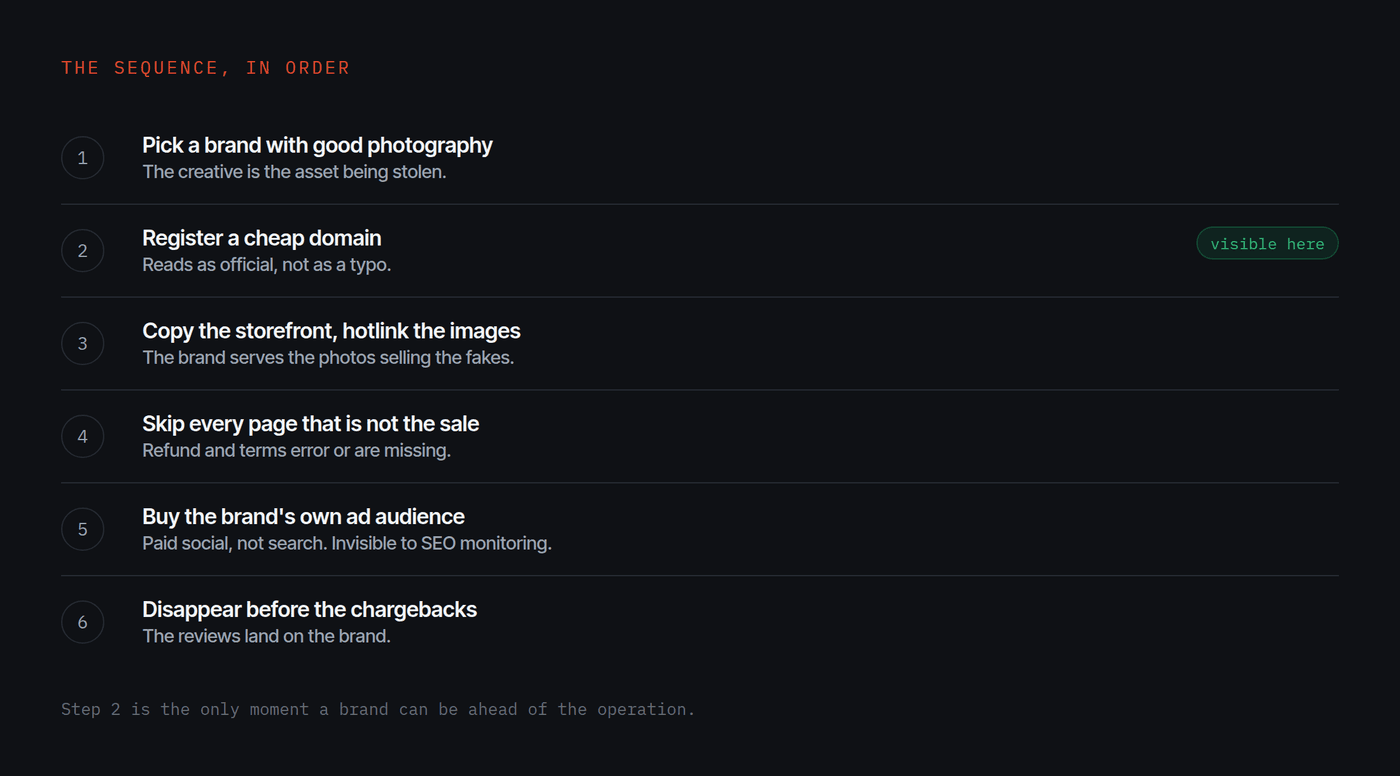
The sequence repeats: pick a brand with good product photography, register a cheap domain that reads as official, copy the storefront and hotlink the images, skip every page that does not contribute to a sale, buy paid social with the brand's own creative, then disappear before the chargebacks land. Search is deliberately avoided.
Step one: pick a brand with catalogue and traffic
The target is not chosen for being vulnerable. It is chosen for having product photography good enough to sell, a catalogue worth copying, and an audience that can be bought. A brand with strong creative is a better target than a brand with weak security, because the creative is the asset being stolen.
Step two: register a cheap domain
The name usually reads as official rather than as a typo. Outlet, official, store, sale, the brand plus a region. The aim is to look like a legitimate second storefront, not to catch someone who mistyped, because the traffic will arrive by advertisement rather than by address bar.
The domain is new, and that is unavoidable. It did not exist before the operator decided to build it, which is why domain age is the first thing worth checking and the hardest thing for a copy to fake.
Step three: copy the storefront
Title, product names, descriptions, structure. Often word for word, occasionally including errors the brand has since fixed on its own site, which is a small and very telling detail: it dates the copy.
The images are the interesting part. Many copies do not download them at all. They link straight to the brand's own content delivery network, so the real brand is serving the product photographs that sell the fake goods, and paying the bandwidth. It is lazy and it is rational, because rehosting a catalogue is work and the store is not built to last.
It also leaves the clearest possible evidence, visible in the page source in seconds.
Step four: skip everything that is not the sale
Refund policy, terms, shipping, contact. Missing, broken, or a generic template with somebody else's company name still in it. None of it contributes to a conversion, and the store is not planning to handle a return.
This is why the footer is one of the fastest checks available to a shopper: a store asking for a card while its refund policy returns an error has answered the question.
Step five: buy the brand's own audience
This is the step most brands miss entirely.
The store does not try to rank. Ranking takes months and the store is not planning to exist for months. It runs paid social, very often with the brand's own product video, targeted at the audience that already responds to that creative.
The consequence is direct. A brand monitoring search results can miss a copy for its entire lifespan, while its customers see it in their feed every day. If you are only watching Google, you are watching the one channel the operation deliberately avoided.
Step six: disappear
Convert what the ad spend buys, then stop. Orders go unfulfilled or arrive as something else. The chargebacks land weeks later, by which time the domain is gone.
The reviews and the support tickets do not land on the operator. They land on the brand, because from the customer's side there was only ever one brand involved.
Where the window actually is
Reading the sequence backwards tells you where detection has to sit.
By the time a customer complains, steps one to six have already happened and the money is gone. By the time the store appears in a search result, if it ever does, the ad campaign is already running.
The one moment that reliably precedes everything is step two. A site that serves HTTPS has to announce its name in a public certificate log before it can take a single order, and that happens before the ads start. That is the only point in the sequence where a brand can be ahead of the operation rather than behind it, and it is why monitoring that watches names rather than complaints is a different thing from monitoring that waits for a customer email.
What taking one down does
It ends that store's revenue and wastes the ad spend already committed. It does not end the operation, because the next domain is a few dollars.
What it changes is the return on copying you specifically. An operator running many brands at once allocates effort to the ones that are cheap. Being the brand whose copies get evidenced and closed within days, rather than discovered by an angry customer in month three, is the only durable form of deterrence available here.
How to catch one in the first week
Reading the sequence backwards, the practical window is the few days between step two, when the domain announces itself, and step five, when the ads start spending. Three habits put you inside it.
- Watch the certificate logs. Every site serving HTTPS publishes its name in a public certificate transparency log before it can take an order, so monitoring those logs for names that look like yours surfaces a copy within hours of it going live. See how to find every domain that looks like yours.
- Watch the Meta Ad Library. Because the copy sells through paid social rather than search, the ads show up in the Meta Ad Library before most other signals. Search your brand name there weekly.
- Watch what the assistants say. A copy an AI assistant starts naming is one already picking up traction. See whether ChatGPT is recommending fake stores instead of your brand.
When you do find one, the first 24 hours guide has the order to work in, and how to take down a fake website covers the routes and the costs.
Catch the next one early
Katcher's free imposter scan finds the storefronts using your brand by matching your product text and image hashes, and shows you the evidence for each one, with no card and no call. It is newer than the enterprise tools and has a smaller takedown track record, and catching a copy in its first days is exactly what it is built for.
About the author
Davis Paipa is the founder of Katcher and of Libautech, and has spent five years building on Shopify. He wrote the playbook down because the step most brands miss, paid social rather than search, is the one that decides whether they ever see the copy.
Questions
Why do copies hotlink images instead of downloading them?
Because it is faster and it costs nothing. Downloading and rehosting a catalogue takes work and storage. Linking straight to the brand's own content delivery network takes none, and the operator is not planning to be around long enough for it to matter.
Why do these stores not appear in search?
Because they are not trying to. Ranking takes months and the store is not planning to exist that long. It buys paid social traffic instead, which is why a brand that only watches search results can miss one entirely.
How long does a copy last?
Not long, by design. The economics work on a short window: build, buy traffic, convert, move. That is what makes detection speed the whole game, because a monthly check will mostly find wreckage.
Does taking one down accomplish anything?
It ends that store's revenue and it costs the operator the ad spend already made. It does not end the operation, because the next domain costs a few dollars. What it changes is the return on copying you specifically.
How do scammers clone Shopify stores?
The sequence is consistent: pick a brand with good product photography, register a cheap domain that reads as official, copy the storefront and often hotlink the images straight from the brand's own content delivery network, skip every page that does not contribute to a sale, buy paid social using the brand's own creative, then disappear before the chargebacks land. They avoid search on purpose, because it is slow and the store is not built to last.
Someone is running a fake dropshipping store using my brand. What do I do?
Capture the evidence first, the page source especially, because a store that serves your product images from your own content delivery network is the clearest proof and it vanishes the moment the store does. Then send the no-signature reports to the host, registrar, CDN and payment processor, and a browser safety report to warn buyers. Because these stores run on paid social, also search the Meta Ad Library for the ads driving traffic to it.
Customers are getting scammed by a fake store using my brand. How do I stop it?
The fastest single action is a browser safety report, which puts a full-page warning in front of anyone about to buy without needing a signature. Then report the host and payment processor so the store cannot take money. For the full order to work in during the first day, see the first 24 hours guide. None of it is permanent, so the durable fix is catching the next copy in its first days rather than after a customer complains.